Say you paid under a hundred dollars for a pair of camera glasses from a marketplace, and the box told you to install an app called HeyCyan. A stranger within Bluetooth range can take over glasses paired through that app without a password. ABC News in Australia published tests showing this on September 22, 2026. Once connected, the attacker can take new photos and video, copy what’s already stored and intercept media on its way to the owner’s phone. The researchers found more than a dozen flaws across the glasses, the app and its website, and most were still open after the developer’s first patches. If your glasses use HeyCyan, the brand printed on the frame doesn’t change any of this.
Six days of testing
Two security firms, NSB Cyber and Abstract Shield, ran the tests for the ABC over six days. They bought one pair from Temu for 60 Australian dollars. The other cost 110 Australian dollars and came from BDI Technology, a Sydney importer, through Big W’s online marketplace. The ABC didn’t publish model names. Similar glasses sold by Dick Smith, Kmart and Amazon in Australia appear to use the same app.
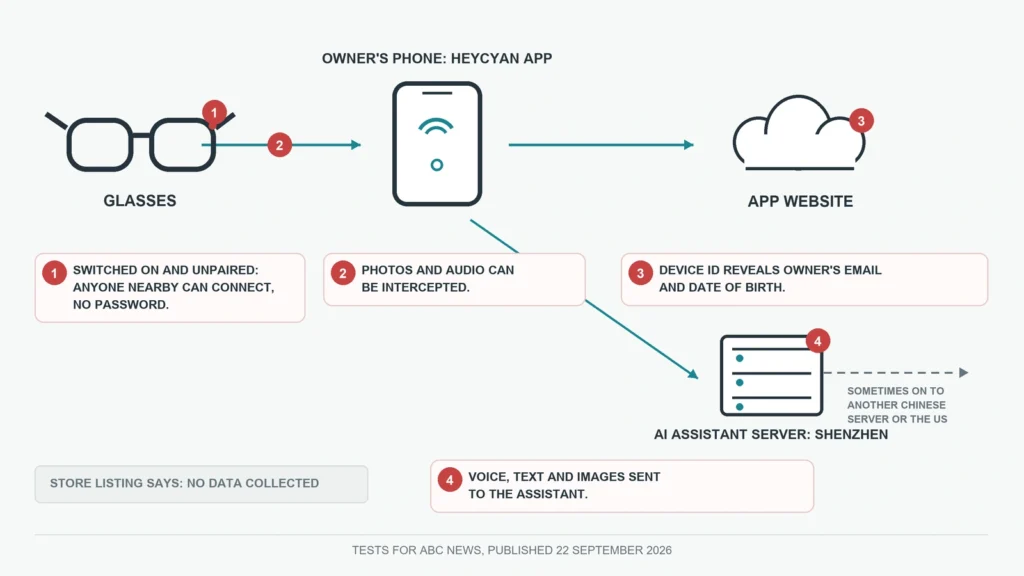
An attacker gets control through a flaw in the pairing. When the glasses are switched on but not connected to the owner’s phone, anyone nearby with the same app can connect first. There’s no password and no button to hold. David Crees, the lead researcher, compared it with earbuds, which make you hold a button for several seconds before a new phone can pair.
The other findings, as the ABC describes them:
- Audio and images can be intercepted while they travel from the glasses to the phone.
- An attacker’s device can pose as your glasses and connect to your app.
- Unpaired glasses broadcast a device ID. A separate flaw on the app’s website returns the owner’s email address and date of birth for that ID.
Where your voice and photos go
The tests found that everything spoken or typed to the built-in AI assistant, and any image sent to it, went first to a server in Shenzhen. Depending on the task, the data could then pass to another Chinese company’s server or to one in the US. The app’s privacy policy names Singapore and doesn’t mention China. Kimberlee Weatherall, a technology law specialist at the University of Sydney, told the ABC that this is hard to justify under Australia’s Privacy Act.
The assistant also gave censored answers. Asked about the persecution of Uyghurs in Xinjiang, it said there was “no credible evidence”, and it declined to discuss Tiananmen Square.
The store listing says no data is collected
The HeyCyan listing on Google Play would mislead an owner checking for themselves. It’s published under the developer name Glasses Dev, and the developer filled in its data safety section. That section says “No data collected” and “Data is encrypted in transit”. The only data it admits sharing is crash logs and diagnostics.
That label doesn’t match what the testers found. Voice and images leave the phone for servers in China, and media moving between the glasses and the phone can be intercepted. Google Play presents these sections as the developer’s own statements.
The listing shows more than 500,000 downloads for HeyCyan, so the problem isn’t confined to Australia. Its September 16, 2026 update said only “Fix bug”, and another update followed on September 29.
Why a patch is unlikely to fix it
The ABC names the app’s developer as Shenzhen Qingcheng Future Technology Co and says the company didn’t reply to repeated requests. After the ABC shared its findings, the developers appeared to patch some flaws, but most remained open.
Crees estimates that about 300 brands of glasses rely on the same app. A fix would mean updating the firmware on every one of them, plus the app and the website. He put that at about a year of work. “The only real solution that I see is a recall,” he told the ABC. BDI Technology says it no longer sells smart glasses, and the ABC understands at least one Australian retailer paused its supply.
Weatherall said the flaws likely breach the Privacy Act, Australian consumer law and the country’s new Cyber Security Act, which has been in force since March.
What to do if you own a pair
If your glasses asked you to install HeyCyan, you’re in the tested group, whatever name is on the box.
The pairing flaw works while the glasses are on and not connected to your phone. Switch them off whenever they aren’t paired with you. Import photos and video to your phone and delete them from the glasses, since stored media is what an attacker can copy. Keep the app updated, though the updates so far have closed only part of the problem.
Treat the AI assistant as a service that sends what you say and show it to servers in China. Don’t show it documents, faces or anything you wouldn’t post publicly. If you haven’t bought yet, a pair on this app is hard to recommend at any price while the pairing flaw stays open. The people you film are the other side of the problem, and our look at how the Dutch regulator treats smart glasses privacy covers them.
Several questions are still open:
- Which retail brands and models use HeyCyan. The 300 figure is the researcher’s estimate.
- Whether the iPhone version of the app behaves the same way. The tests the ABC describes don’t say.
- Whether the fixes are complete. A lawyer for the company told the ABC that engineers had fixed the flaws. As of October 2, the testers found that many fixes hadn’t worked or were incomplete.
- Whether regulators outside Australia will act. On October 7, 2026, Australia’s Information Commissioner announced an investigation into the privacy practices of Shenzhen Qingcheng, the app’s maker.